The cve.tools Blog
Product updates, the weekly threat signal, and monthly trends: what shipped, what's exploited, and where we're heading.
- The Dialer Nobody Turns On: CVE-2026-20230 Still Gave Attackers Root on Cisco Unified CMCisco Unified Communications Manager (Unified CM) is the call-processing brain behind enterprise VoIP — the box that routes calls, holds the dial plan, and talks to every phone, gateway and trunk…CVE-2026-202307 min
- The one button I click on a CVE page — and what it does afterYou're reading one CVE. The Watch button asks for one click and no signup, then remembers the product for you. It's the easiest on-ramp to My Stack — and I'll be honest about why it's a garnish, not the way to build a whole inventory.CVE-2023-49663 min
- Meet OWAReaper: The Grim Reaper's Evil Twin That Survives Your Incident ResponseEvery horror franchise eventually runs out of new monsters and reboots the old one with a smaller budget and a meaner attitude. Sequels rarely improve on the original — they're usually cheaper,…CVE-2026-428978 min
- CVE-2026-20079: the 10.0 auth-bypass that shares a footprint with the FMC bug already under attackPicture the one box in your network whose whole job is to be trusted. Not a firewall — the thing that programs the firewalls: the management center that pushes policy, signatures and access rules…CVE-2026-200799 min
- N-able N-central Auth-Bypass Chain (CVE-2026-18577) Exploited in the Wild — Patch NowThe U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-18577, an authentication-bypass flaw in N-able's N-central remote monitoring and management platform, to its Known…CVE-2026-185775 min
- NVD Can't Agree With Itself on CVE-2026-34486 — And an AI-Run Hacking Crew Was Already Using ItOn August 4, 2026, CISA added CVE-2026-34486 — a bypass of Apache Tomcat's cluster-traffic encryption — to the Known Exploited Vulnerabilities catalog, alongside an IBM Langflow RCE and an N-able…CVE-2026-344867 min
- JetBrains TeamCity's unauthenticated 9.8: CVE-2026-63077 turns the channel you trust into RCEOn July 27, 2026, JetBrains disclosed CVE-2026-63077 — an unauthenticated remote code execution flaw in TeamCity On-Premises. It is rated CVSS 9.8, and all an attacker needs is network reach to…CVE-2026-630775 min
- The guardian is the gateway: 2026's exploited-bug list is a map of the security products we trustedThere is a comfortable story we tell ourselves: buy a security box, and the attack surface gets smaller. For most of 2026, the exploited-in-the-wild list has been telling a different one. The guardians are the gate now — and the common thread across the year's most-attacked machines isn't a bug class, it's a target class.CVE-2026-203168 min
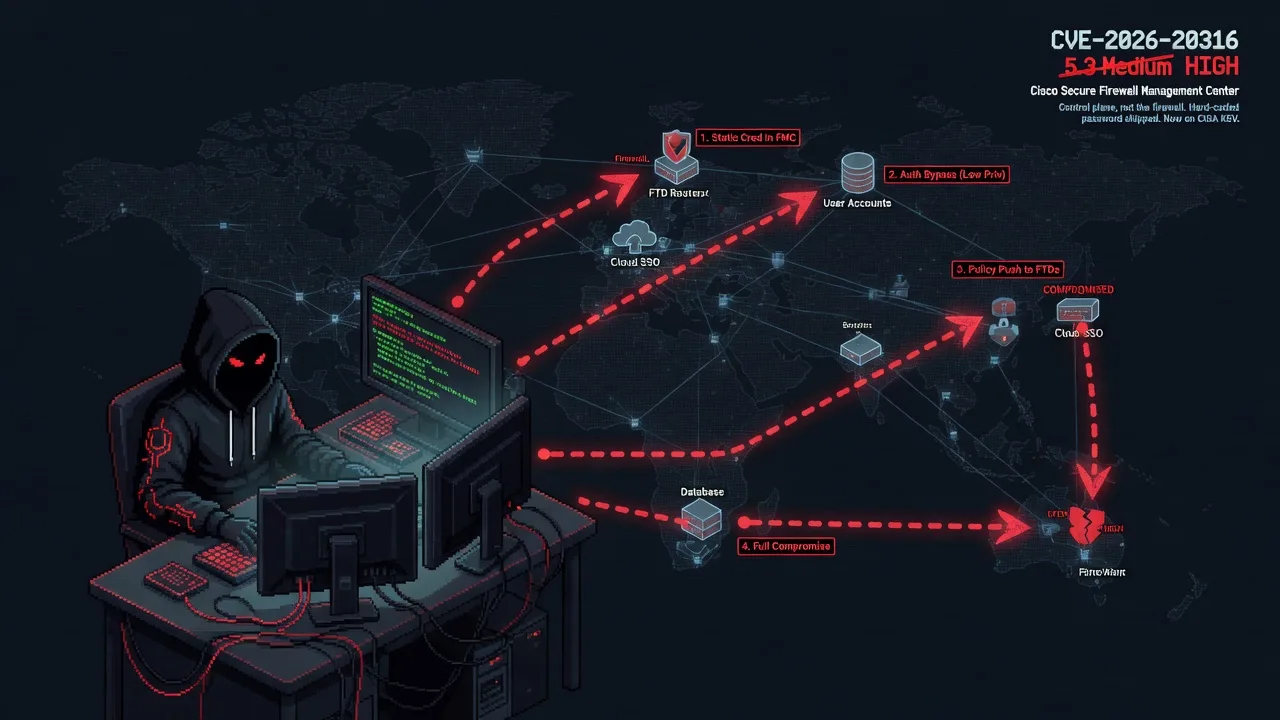
- Cisco's firewall brain ships a hard-coded password: CVE-2026-20316 is the 5.3 that landed on CISA's KEV listCisco Secure Firewall Management Center (FMC) is not a firewall. It is the control plane — the console that pushes policy, rules and software to every Firepower Threat Defense (FTD) box in your…CVE-2026-203165 min
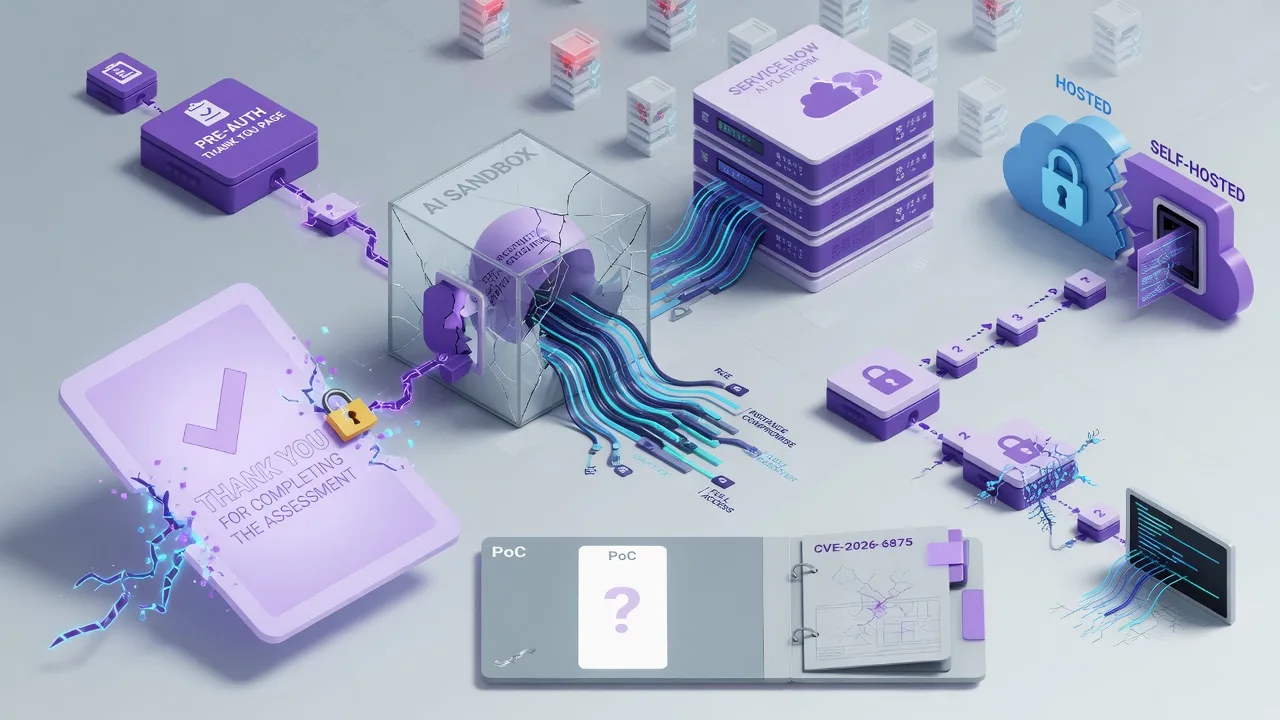
- The Politest RCE: A Pre-Auth "Thank You" Page Escaped ServiceNow's AI Sandbox (CVE-2026-6875)CVE-2026-6875 is an unauthenticated sandbox escape in the ServiceNow AI Platform that turns a pre-auth "thanks for completing the assessment" page into full instance compromise. Here's the escalating chain, the hosted-vs-self-hosted split, and why the exploit index looks quiet while EPSS sits in the 97th percentile.CVE-2026-68758 min
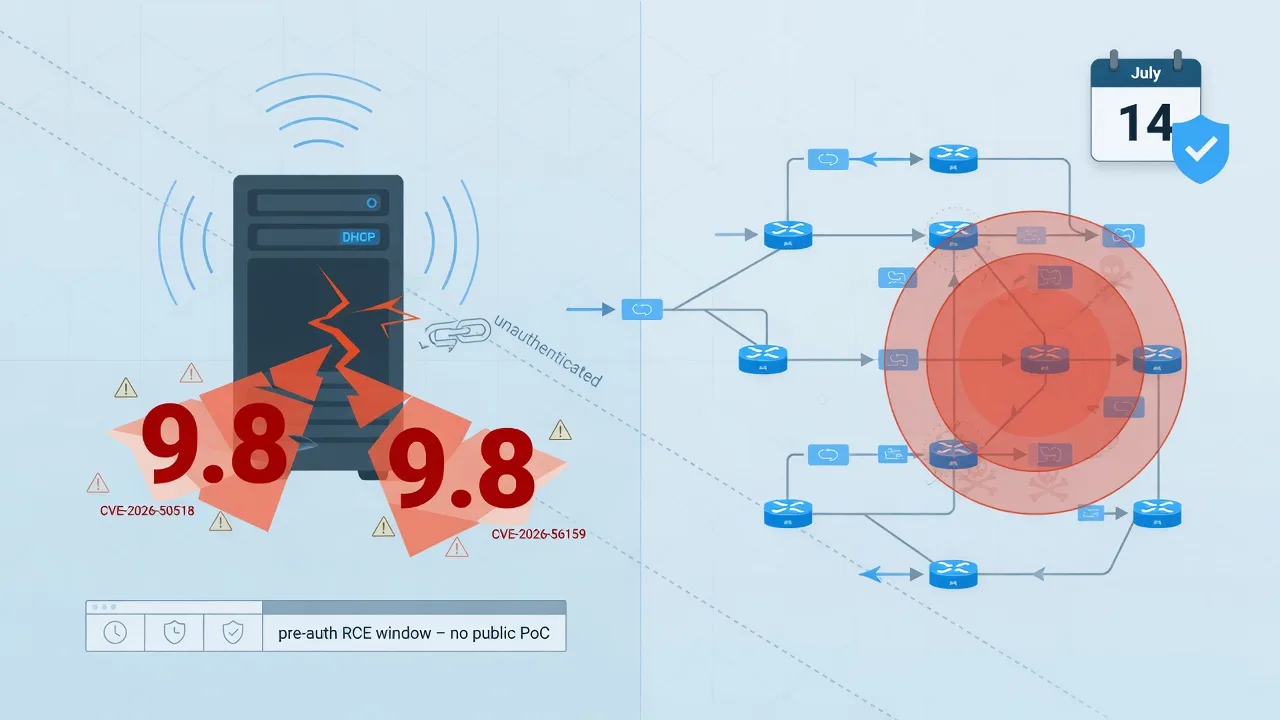
- Two 9.8s in Windows DHCP Server: the unauthenticated heap-overflow RCEs hiding in July's Patch TuesdayMicrosoft's July 14 Patch Tuesday quietly fixed two CVSS 9.8 unauthenticated RCEs in Windows DHCP Server. Here's why a memory-corruption bug in core network infrastructure is a worst-case blast radius — and how to triage it before a public exploit exists.CVE-2026-505186 min
- Oracle's July CPU Dropped Five 9.8 WebLogic RCEs at Once — Patch During the Quiet WindowEvery quarter Oracle ships a Critical Patch Update, and every quarter a little part of me braces before opening the advisory — it's a wall of hundreds of fixes across products most of us have never…CVE-2026-601988 min
- Stop typing your software inventory. Import it in one command.A real environment is hundreds of products across dozens of versions. You don't type that. Here's the CLI: scan a host, import an SBOM, or run an ad-hoc 'am I affected?' check from CI — with a local-only option that never uploads your inventory.CVE-2021-442285 min
- Splunk Enterprise's open sidecar: the unauthenticated 9.8 that turns your SIEM into a foothold (CVE-2026-20253)CVE-2026-20253 is an unauthenticated arbitrary file-write in a PostgreSQL sidecar service that Splunk Enterprise 10.x ships alongside Edge Processor, OpAmp and SPL2 pipelines. It scores CVSS 9.8, sits at the 99.87th EPSS percentile, and is on CISA KEV with limited in-the-wild exploitation confirmed. Here's the missing-auth root cause, the exact affected versions, and how to patch — or disable the sidecar — without losing features.CVE-2026-202536 min
- Cisco baked a password into your firewall manager: CVE-2026-20316Cisco Secure Firewall Management Center ships with a hard-coded, low-privilege account. It scores CVSS 5.3 - but it is actively exploited, KEV-listed, and Cisco rates it High because it chains to privilege escalation on the box that manages your firewalls.CVE-2026-203168 min
- No autoType, No Gadget, Still RCE: Inside the fastjson 1.x Zero-Day (CVE-2026-16723)CVE-2026-16723 is a CVSS 9.0 RCE in fastjson 1.2.68-1.2.83 that needs no autoType and no classpath gadget, is being actively exploited, and is fixed in 1.2.84. Exploit chain, exposure check, detection rules and remediation.CVE-2026-167238 min
- VeloCloud Orchestrator under attack: CVE-2026-16812 is an unauthenticated 10.0 RCECVE-2026-16812 is a CVSS 10.0, unauthenticated OS command-injection flaw in VeloCloud Orchestrator On-Prem. Here's the chain, who's affected, the fixed builds, and how to detect and remediate it.CVE-2026-168128 min
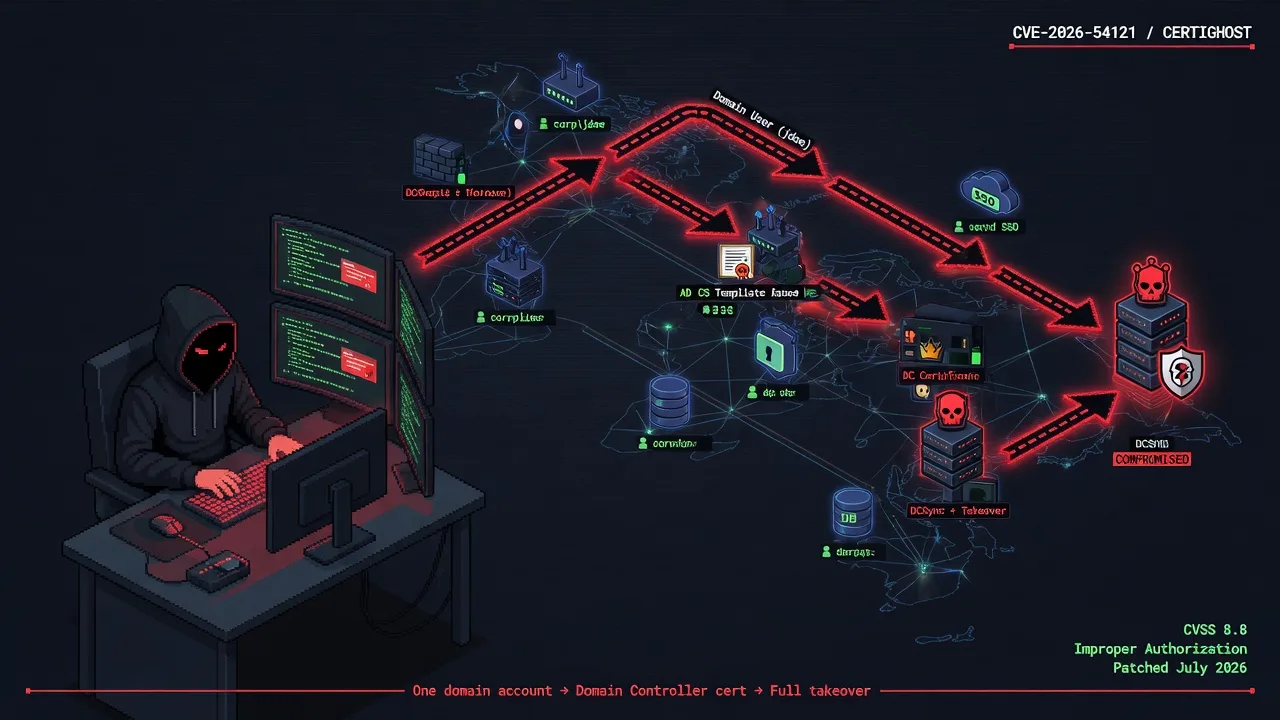
- Certighost: how one domain account turns AD CS into a Domain Controller (CVE-2026-54121)With one ordinary domain account and no admin rights, CVE-2026-54121 ("Certighost") makes an AD CS Certificate Authority issue a Domain-Controller-identity certificate -- a straight line to DCSync and domain takeover. Here's the chain, how to detect it, and how to fix it.CVE-2026-5412110 min
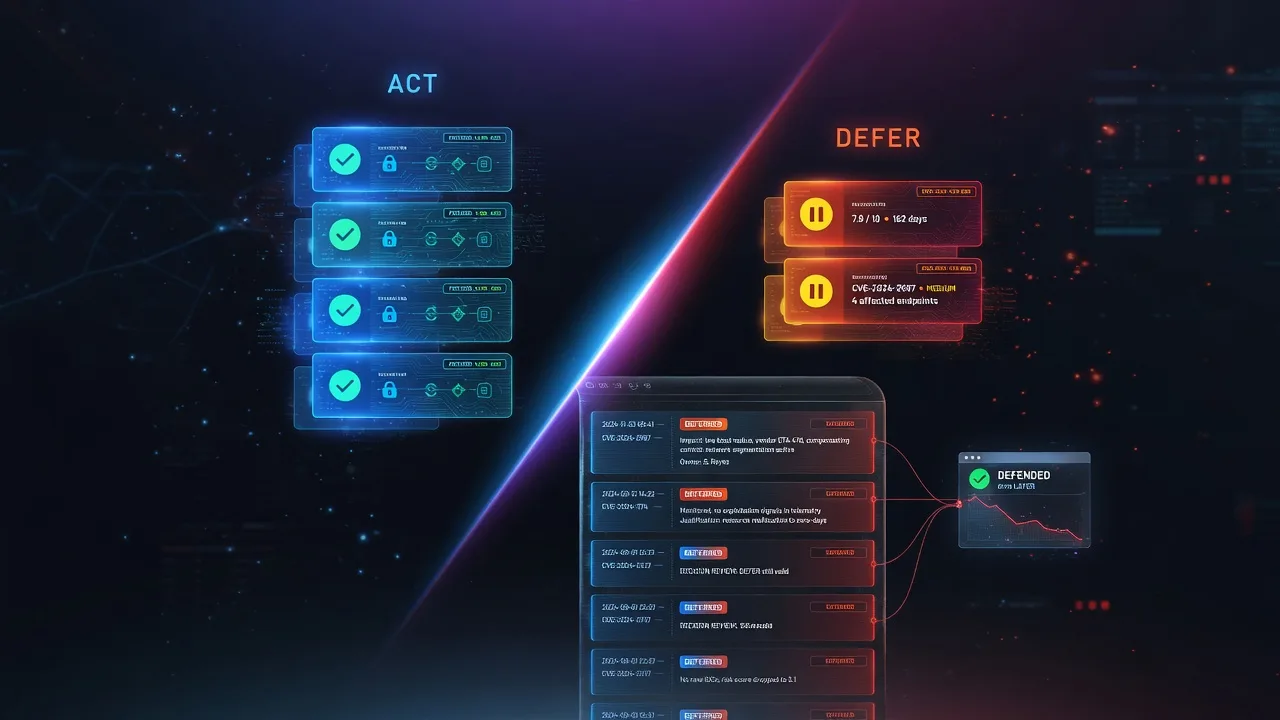
- Patch the few that matter — and prove you were right to defer the restNobody patches everything. The hard part isn't the ACT pile — it's defending the DEFER pile six months later. Here's how I use My Stack's cut-line policy and append-only decision ledger to do exactly that.CVE-2023-49665 min
- Zimbra's half-click XSS: how a CSS trick let Russian spies read government mail (CVE-2025-66376)CVE-2025-66376 is a stored XSS in Zimbra's Classic Web Client - a CSS @import trick that runs JavaScript when you open an email. A Russian-aligned actor used it as a zero-day to steal government mail and 2FA codes. What it is, how the chain works, how to detect it, and how to evict it.CVE-2025-6637612 min