The cve.tools Blog
Product updates, the weekly threat signal, and monthly trends: what shipped, what's exploited, and where we're heading.
- MLflow's SSRF Bypass Was Being Scanned Within Hours — And CISA Added It to KEV Two Days LaterMLflow validates a webhook's URL once, then follows redirects without re-checking where they lead — enough to turn an unauthenticated /test endpoint into a full-read path to AWS instance metadata. CISA added it to KEV two days after publication, on watchTowr honeypot evidence, despite an EPSS score in the 63rd percentile and zero public exploit code in our own index.CVE-2026-648496 min
- Head Mare Weaponized TrueConf's Own Video-Call Client to Backdoor Its Users — CISA Added Both Bugs to KEV a Week After DisclosureOn August 19-20, 2026, CISA added two TrueConf Server vulnerabilities to its Known Exploited Vulnerabilities catalog. TrueConf is a video-conferencing platform widely deployed across Russian industry…CVE-2026-725297 min
- Langflow's Auto-Login Endpoint Was Handing Out Admin Tokens — CVE-2026-9198 Has Been Under Attack Since Before It Had a CVELangflow is an open-source visual builder for LLM-powered agents and workflows — the kind of tool a team stands up to wire together model calls, retrieval steps, tool invocations and database…CVE-2026-91986 min
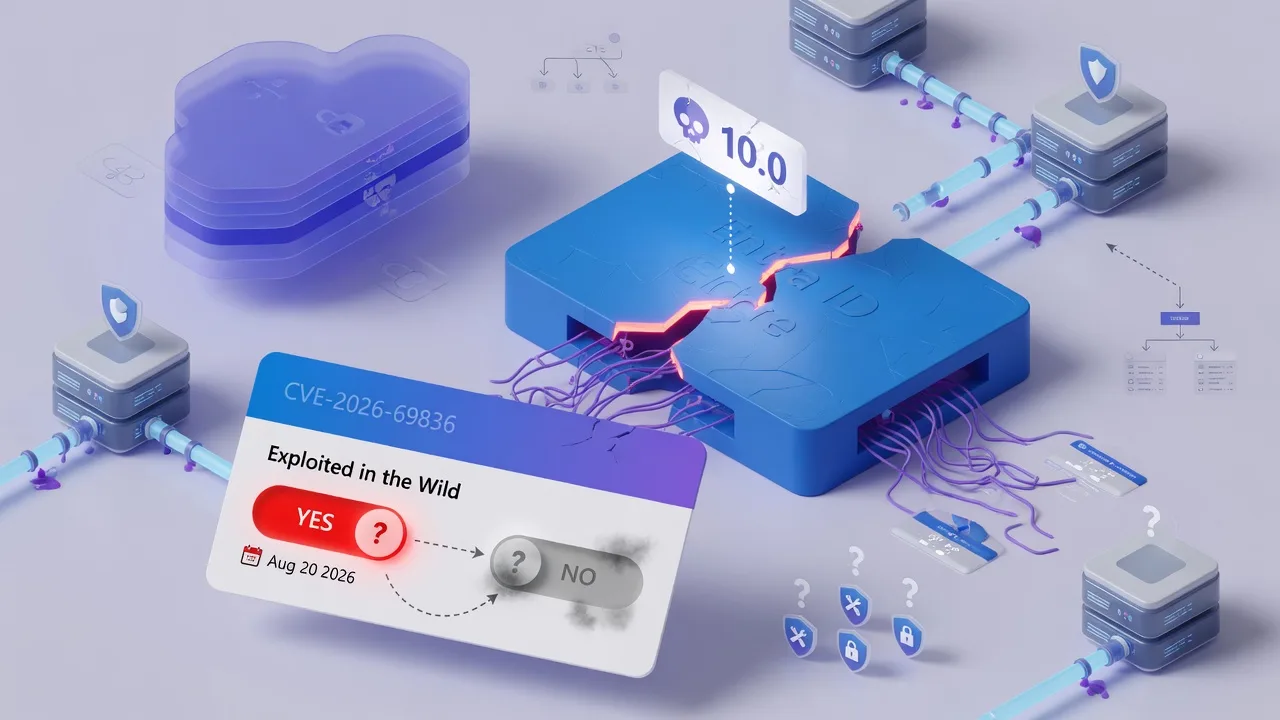
- Microsoft Called Its Own Entra ID Bug "Exploited." Then It Didn't.On August 20, 2026, Microsoft published an advisory for CVE-2026-69836, a deserialization bug in Entra ID — its cloud identity service — carrying the maximum possible CVSS score: 10.0. The…CVE-2026-698366 min
- Zimbra's Optional SNMP Package Turned Into an Unauthenticated RCE — and CERT Polska Caught It ExploitedOn July 20, 2026, Zimbra quietly shipped Collaboration Suite 10.1.20 with a fix for an unauthenticated remote code execution bug. For about a month, nothing happened publicly. Then, in the week of…CVE-2026-735705 min
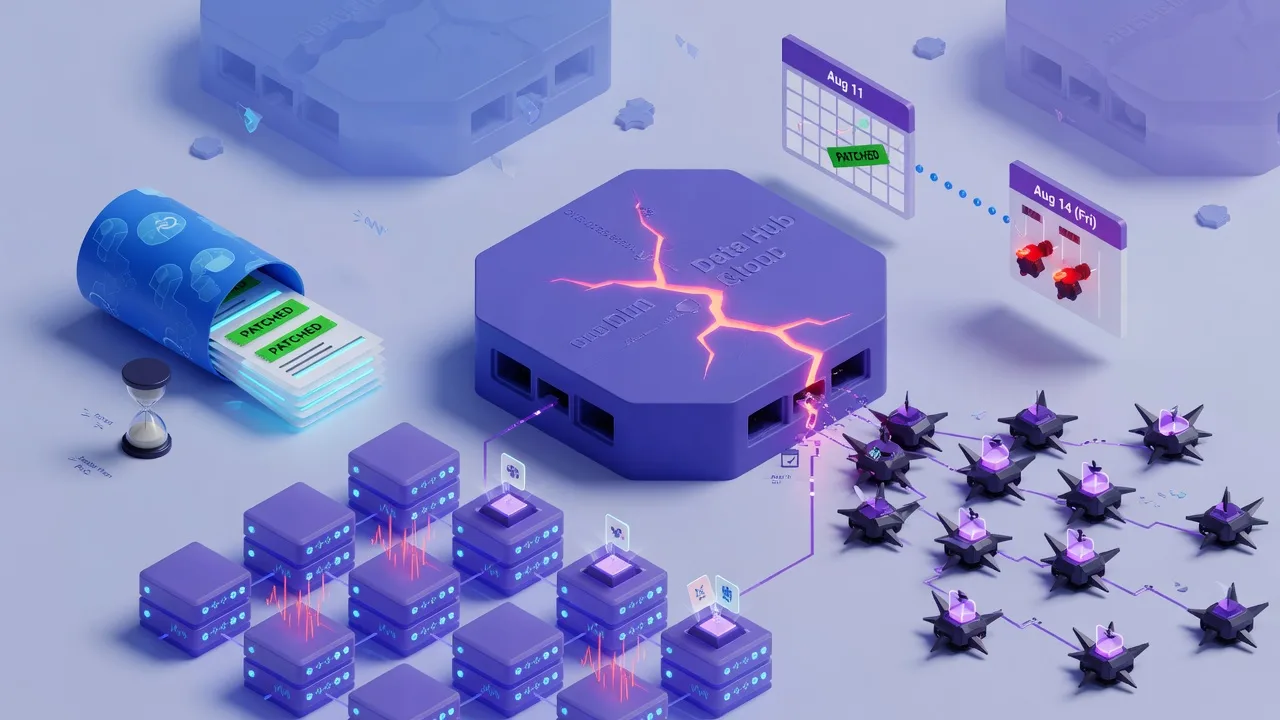
- SAP Commerce Cloud's CVSS 10.0 Data Hub Bug: Exploitation Attempts Started Three Days After the PatchOn August 11, 2026, SAP's monthly Patch Day fixed CVE-2026-58231: a maximum-severity flaw in SAP Commerce Cloud's Data Hub Adapter that lets a fully unauthenticated attacker abuse a default…CVE-2026-582317 min
- ChainDrop: The npm Worm That Made "Verified" Code MeaninglessNo CVE was assigned because nothing in keyv's code was vulnerable — a maintainer identity was compromised, and the build pipeline faithfully signed the malicious result. ChainDrop then used stolen npm tokens to spread itself into 1,300+ more package versions.6 min
- GeoServer's jsonArrayContains Zero-Day: Attackers Moved Faster Than the PatchOn August 12, 2026 at 10:46 UTC, a researcher going by @q1uf3ng posted a message on X describing an unauthenticated SQL injection in GeoServer's jsonArrayContains filter function — and noted that,…CVE-2024-364017 min
- The Firewall Crash Bug Cisco Has Now Shipped Twice: CVE-2026-20349 and Its 2024 TwinOn August 11, 2026, Cisco disclosed CVE-2026-20349: an unauthenticated, remotely triggerable denial-of-service flaw in the Remote Access SSL VPN service of Secure Firewall ASA and Threat Defense…CVE-2026-203496 min
- macOS Screen Sharing Flaw CVE-2026-65400 Hits CISA's KEV List as Attackers Mine Monero on Exposed MacsOn August 6, 2026, Apple quietly fixed a bug in macOS Screen Sharing and it was rated CVSS 7.1 — high, not urgent. Eight days later, CISA rewrote the score to 9.8 critical, with no new technical…CVE-2026-654006 min
- Lazarus Just Exploited the Same Windows Driver It Weaponized Two Years AgoMicrosoft's August 11, 2026 Patch Tuesday fixed 421 CVEs. Only one was flagged as actively exploited: CVE-2026-68820, a use-after-free in the Windows Ancillary Function Driver for WinSock —…CVE-2026-688207 min
- The Router Bug DD-WRT Patched in 2021 Just Became a Botnet's Front DoorDD-WRT fixed CVE-2021-27137 within days of being told about it, back in March 2021. Nobody wrote it up as a big deal — the flaw needed UPnP enabled (off by default) and, per the researcher's own…CVE-2021-271377 min
- The Password Reset Endpoint That Gave Away Admin: Metabase's CVE-2026-72898 and the Four Companies Behind ItAn unauthenticated SQL injection in Metabase's password-reset endpoint let attackers reach full admin on internet-facing instances — and pivot into every database credential Metabase stored. Metabase's own Cloud got hit first; Framework, Tally, n8n and Kilo Code disclosed downstream breaches within days.CVE-2026-728986 min
- EPSS vs CVSS vs KEV: which number actually tells you to patchCVSS is severity, KEV is confirmed exploitation, EPSS is probability. They answer different questions and the moment you equate them you start patching the wrong CVEs. A field guide, plus how the three become a single cut-line in My Stack.CVE-2023-444874 min
- NatJack: The Same NAT Flaw Got Windows and Linux Patched — Cisco and Apple Call It a FeatureOn August 6, 2026, at Black Hat USA, Synack Red Team researcher Malcolm Stagg told the room that the trust model underneath nearly every NAT device on the planet is broken. Two vendors listened and…CVE-2026-561817 min
- Two Parsers, One File, Zero Agreement: The Attack Surface Behind CVE-2026-66066Here's the question worth asking whenever a framework bolts on "free" image processing: if the web layer checks a file's label, and a native image library checks its bytes, who actually decides what…CVE-2026-660669 min
- Veeam ONE's CVSS 10.0 Unauthenticated RCE Targets the Box That Watches Your BackupsOn August 4, 2026, Veeam published KB4892 disclosing six vulnerabilities in Veeam ONE — the monitoring and reporting layer that sits across an organization's backup and virtualization estate. The…CVE-2026-646336 min
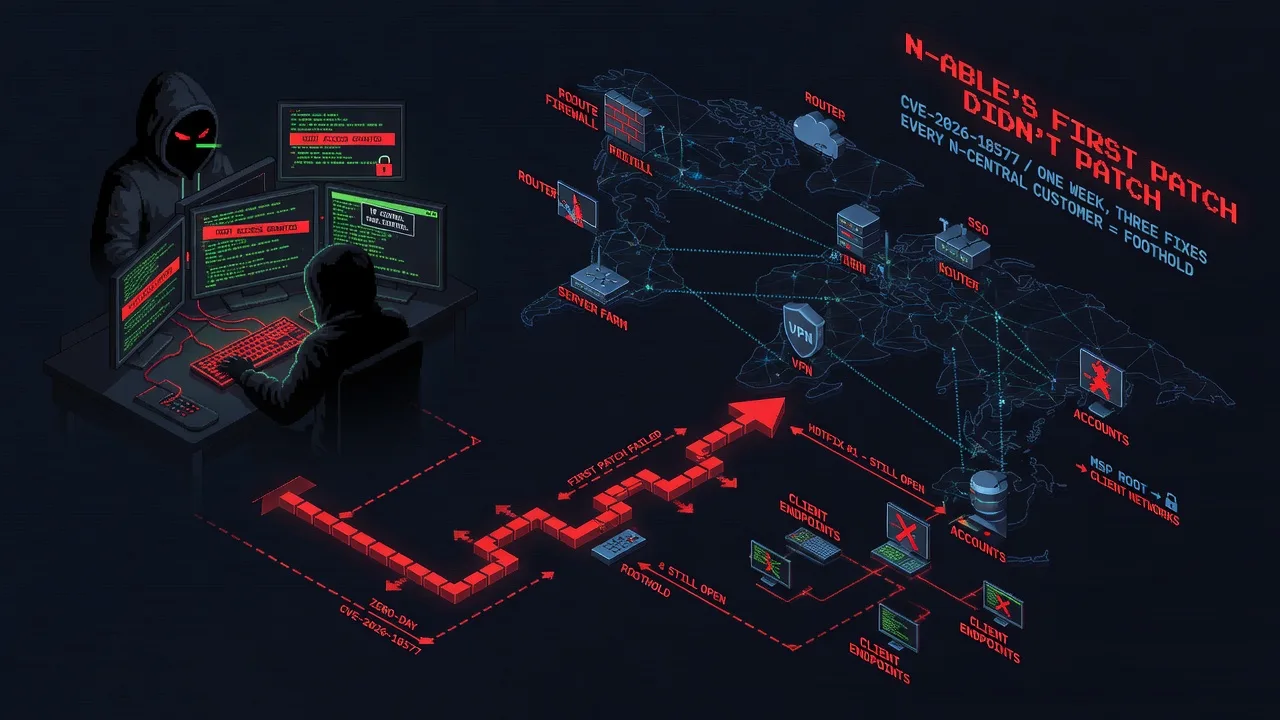
- N-Able's First Patch Didn't Patch — CVE-2026-18577 Turns Every N-central Customer Into a FootholdN-central is the console MSPs use to manage hundreds of client networks from one screen — patching, monitoring, and, critically, a built-in remote-access feature called Take Control. That design is…CVE-2026-185777 min
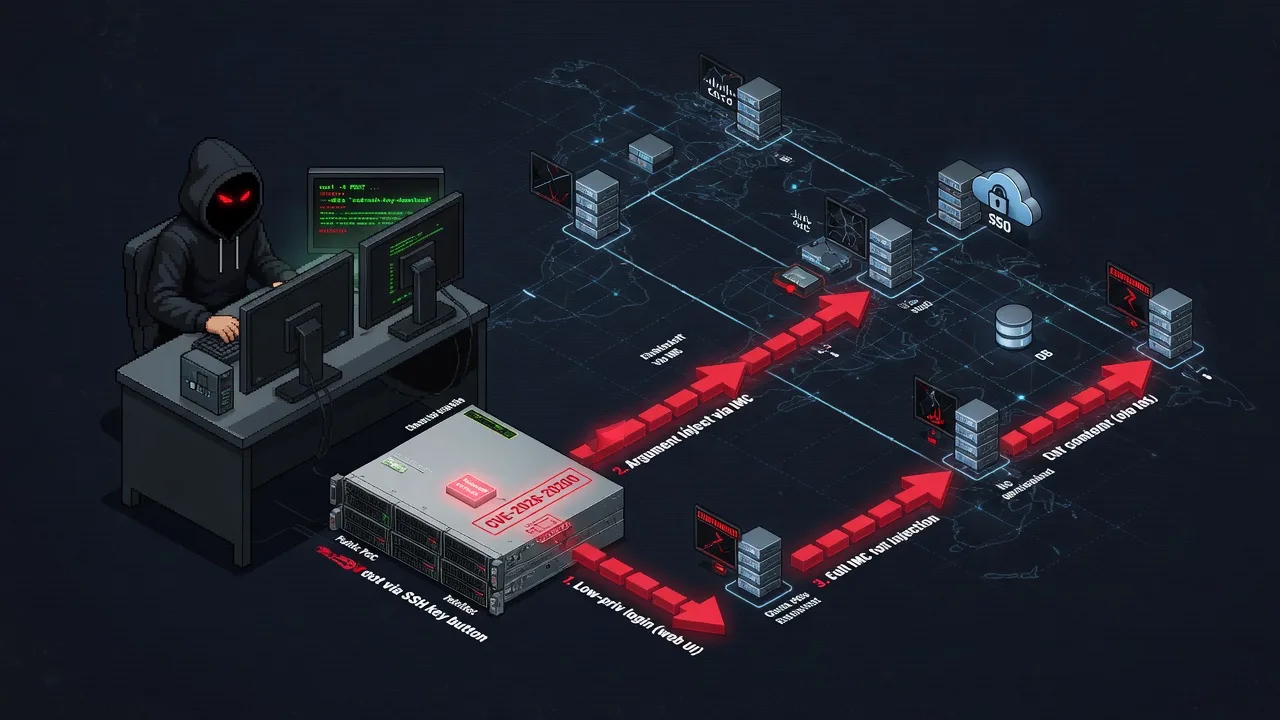
- Cisco's rack-server controller sat below the OS — CVE-2026-20200 turns a "download my SSH key" button into root, with a public PoC already outCisco Integrated Management Controller (IMC) is the out-of-band console welded to every UCS rack server — the thing you reach when the operating system on top of it is unresponsive, unbootable, or…CVE-2026-202008 min
- Broadcom's VMSA-2026-0006 Patches Three Critical VMware Flaws — vCenter Has Failed This Exact Way BeforeOn July 29, 2026, Broadcom shipped VMSA-2026-0006, patching five vulnerabilities across VMware ESX, vCenter, Workstation and Fusion. Three are rated Critical and read like a greatest-hits list of…CVE-2026-593096 min