
The cve.tools Blog
Product updates, the weekly threat signal, and monthly trends: what shipped, what's exploited, and where we're heading.
- LiteLLM RCE (CVE-2026-42271): when an MCP "test connection" button spawns a shellLiteLLM's MCP preview endpoints accepted a full stdio server config — command, args, env — and dutifully spawned it as a subprocess on the proxy host, gated by nothing but a valid API key. CVE-2026-42271 is authenticated remote command execution on your AI gateway. Here's the mechanism, who's exposed, and what to do today.CVE-2026-422714 min
- CVE-2026-33017: the Langflow public endpoint that runs your code without a loginA single unauthenticated HTTP POST is enough to run your code on an internet-facing Langflow server. The endpoint POST /api/v1/buildpublictmp/{flowid}/flow is meant to be public — it builds public…CVE-2026-3301710 min
- CVE-2026-61447: the PraisonAI agent that runs the model's code - with your secrets attachedMost remote code execution bugs are about a parser you didn't know was reachable. CVE-2026-61447 is stranger and more modern: the component is designed to run code, and the code comes from a language…CVE-2026-6144711 min
- CVE-2026-48908: the anonymous Joomla upload that hands over the whole serverOne anonymous HTTP request is the whole exploit. SP Page Builder exposes an upload task, asset.uploadCustomIcon, that shipped with no authentication, no anti-CSRF token, and no server-side file-type…CVE-2026-489089 min
- Langflow's quiet IDOR: run anyone's flow, steal the secrets inside it (CVE-2026-55255)CVE-2026-55255 lets any logged-in Langflow user execute another user's flow and coax out its embedded LLM, cloud and database secrets. EPSS is low, but it's on CISA KEV and exploited in the wild. Here's the chain, who's exposed, and how to shut it.CVE-2026-552558 min
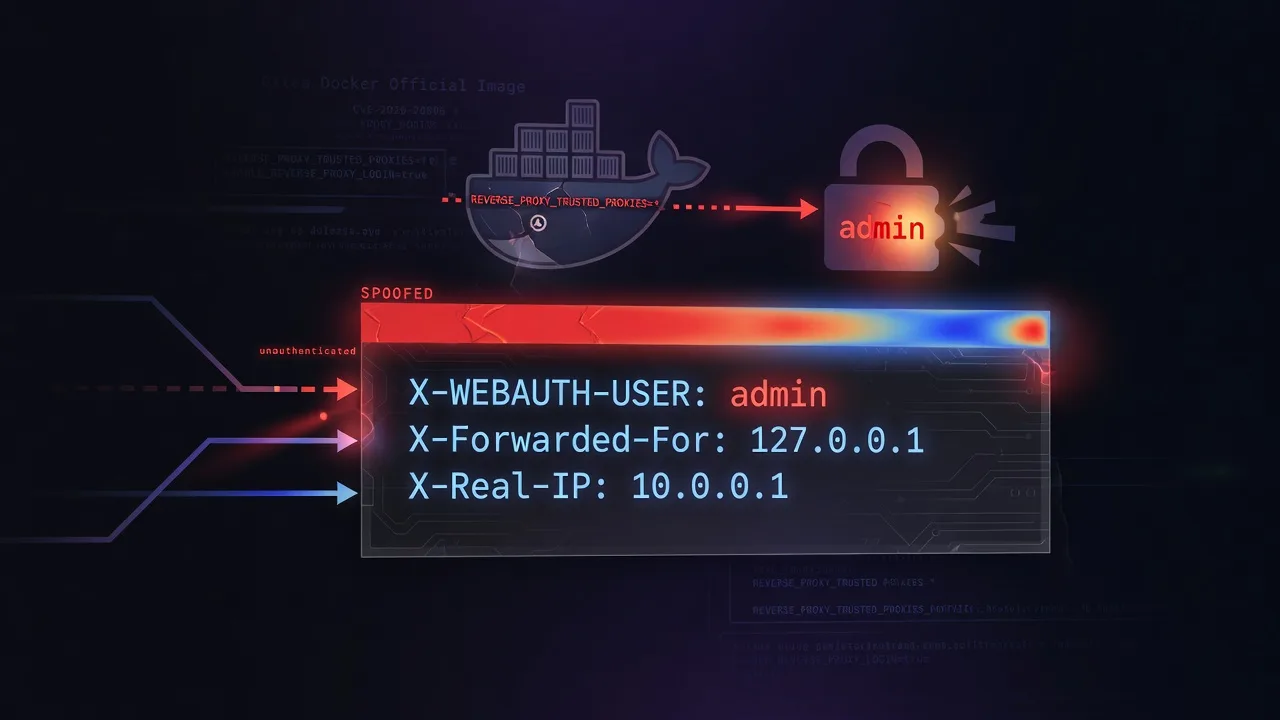
- One HTTP header, any Gitea user: inside CVE-2026-20896The Gitea Docker image shipped REVERSE_PROXY_TRUSTED_PROXIES=* by default. On instances that enabled reverse-proxy login, an unauthenticated request carrying X-WEBAUTH-USER: admin was enough to take over. Here is exactly how it works, who is actually exposed, and how to shut it down.CVE-2026-208968 min
- CVE-2026-48282: the max-severity ColdFusion RDS path traversal that became RCE in 48 hoursThe flaw lets an attacker abuse ColdFusion's RDS file handler to write a file outside the directory it should be confined to -- and because the file lands in a web-reachable folder as executable…CVE-2026-4828211 min
- CVE-2021-29441: the Nacos backdoor you open by lying about your User-AgentCVE-2021-29441 lets anyone who can merely reach an Alibaba Nacos server perform any administrative action with no credentials. The flaw lives in the AuthFilter servlet filter, which was built with a…CVE-2021-2944111 min
- Now you can shape CVE Tools — feedback in one clickTwo new ways to be part of CVE Tools: leave feedback on any page in one click, and get notified — in the app and on your device — when something you care about happens.3 min
- How to find out which vulnerabilities you actually haveThere are over 340,000 published CVEs, and more land every day. Scroll any feed and it's a wall of severity badges. But almost none of them are your problem — and the ones that are, you can rarely…12 min
- CVE-2025-3248: the Langflow endpoint that 'validates' your code by running itCVE-2025-3248 lets anyone who can merely reach a Langflow server execute code on it with no credentials. The bug lives in POST /api/v1/validate/code -- an endpoint whose entire job is to check…CVE-2025-324810 min
- CVE-2026-45659: the 'forgotten' SharePoint deserialization RCE that CISA just flagged as exploitedThe flaw lets an authenticated SharePoint user send a crafted, malicious object to the server and have it run code -- classic untrusted-data deserialization. It is not the unauthenticated 2025…CVE-2026-456599 min
- Make triage calls you can defend — plus a sharper CVSS toolHey there 👋 This was a big one. Over the past few days your Stack turned into a real triage console, the CVSS page became a full toolkit, the homepage got a ground-up rewrite, and we added a…4 min
- CVE-2026-8037: the pre-auth heap bug that hands out root on Progress LoadMasterCVE-2026-8037 lets an attacker who can merely reach a Progress LoadMaster's management API execute operating-system commands on the appliance as root, with no credentials. The bug lives in the API…CVE-2026-80379 min
- Cacti's rfilter SQL injection is back: a pre-auth 9.8 in graph_view.php (CVE-2026-39893)Cacti is the open-source performance and fault-monitoring framework that ISPs and enterprises use to graph network health — SNMP polling, RRDtool graphs, the works. CVE-2026-39893 lives in its…CVE-2026-3989311 min
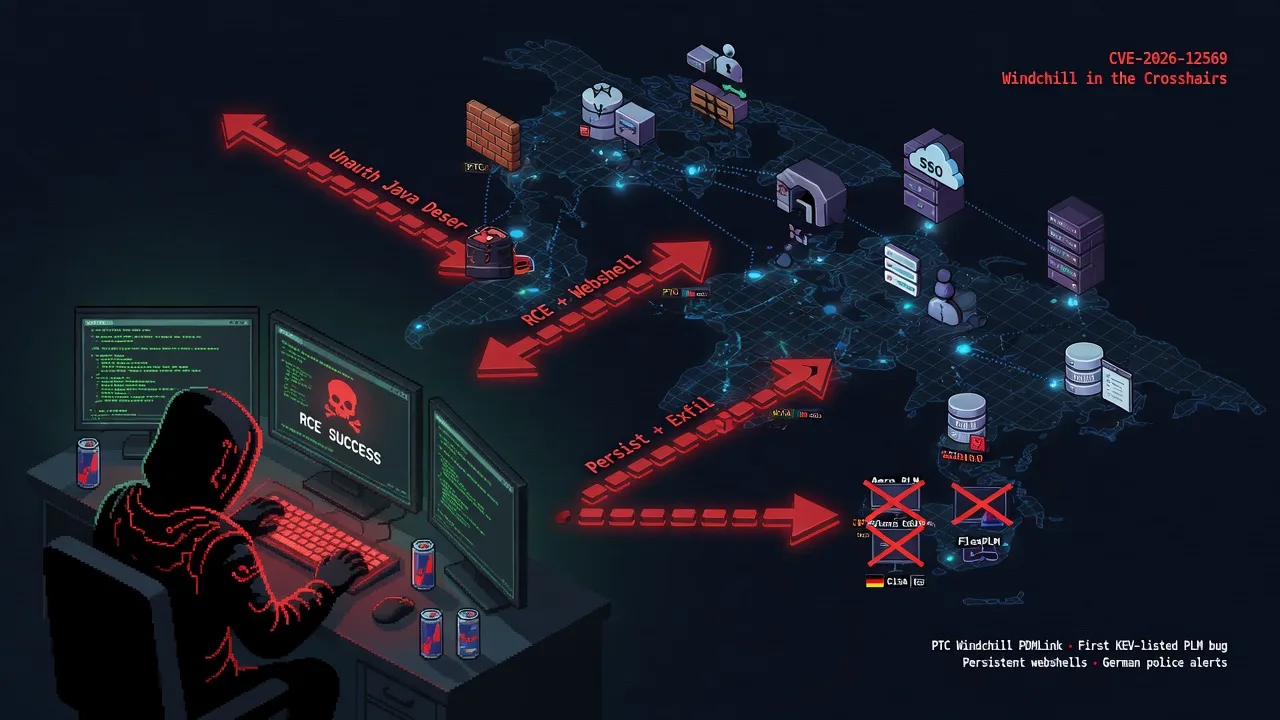
- Windchill in the crosshairs: CVE-2026-12569, the first PTC bug in CISA's KEVProduct lifecycle management (PLM) software rarely makes security headlines — but it holds the crown jewels: the CAD models, bills of materials, and manufacturing specs of aerospace, defense,…CVE-2026-125696 min
- CVE-2025-61882: the unauthenticated Oracle EBS pre-auth RCE that Cl0p turned into a data-theft campaignCVE-2025-61882 lets an attacker who can merely reach your Oracle E-Business Suite web tier run code on it -- no login, no user interaction. It is not theoretical: it powered a mass data-theft and…CVE-2025-618828 min
- CVE-2026-46817: the unauthenticated Oracle EBS file read that leaks your payment secretsCVE-2026-46817 lets an attacker who can merely reach your Oracle E-Business Suite over HTTP read files off the server -- no login, no user interaction. The bug lives in the Oracle Payments (iPayment)…CVE-2026-468178 min
- CVSS Calculator: How to Read a Vulnerability Score — and Why It Isn't Your RiskA CVSS calculator turns a vector into a 0–10 number in a second — the trap is treating that number as your risk. Here's how to read the score, recompute it for your environment, and layer EPSS and CISA KEV on top to actually prioritize.CVE-2026-202457 min
- Clearer CVE explainers, and a blog with diagramsHey there 👋 The last few days were all about making the why clearer — a sharper read on what a CVE actually means, and a proper home for these very updates. Here's what landed.3 min